

DNS
Child Nameservers vs. External Zone Delegation Explained
Learn how child nameservers, glue records, and subdomain delegation work, where each is configured, and when to use one over the other.
Learn how child nameservers, glue records, and subdomain delegation work, where each is configured, and when to use one over the other.

A DNS amplification attack spoofs the victim's IP to trigger massive reflected responses from open resolvers, using EDNS0's larger buffer sizes (up to 4096 bytes) to turn a 60-byte request into a 3,000-byte response, roughly 50x amplification. Mitigation includes Response Rate Limiting, closing open recursion, and upstream scrubbing.

Learn the difference between recursive DNS resolvers and authoritative nameservers, how caching works, and where each fits in a DNS lookup.
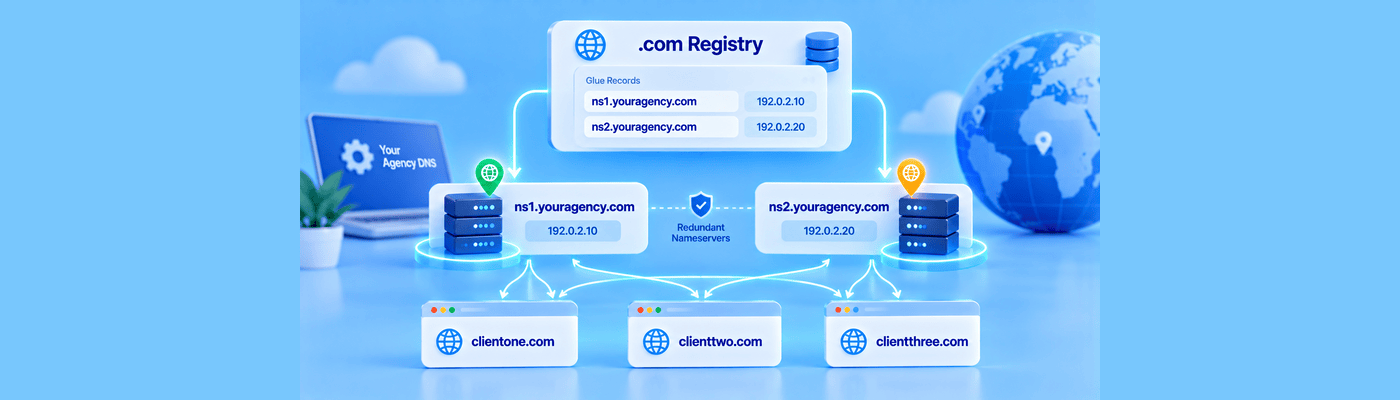
Learn how glue records work, why custom nameservers need them, and how agencies can configure branded nameservers such as ns1.yourdomain.com.
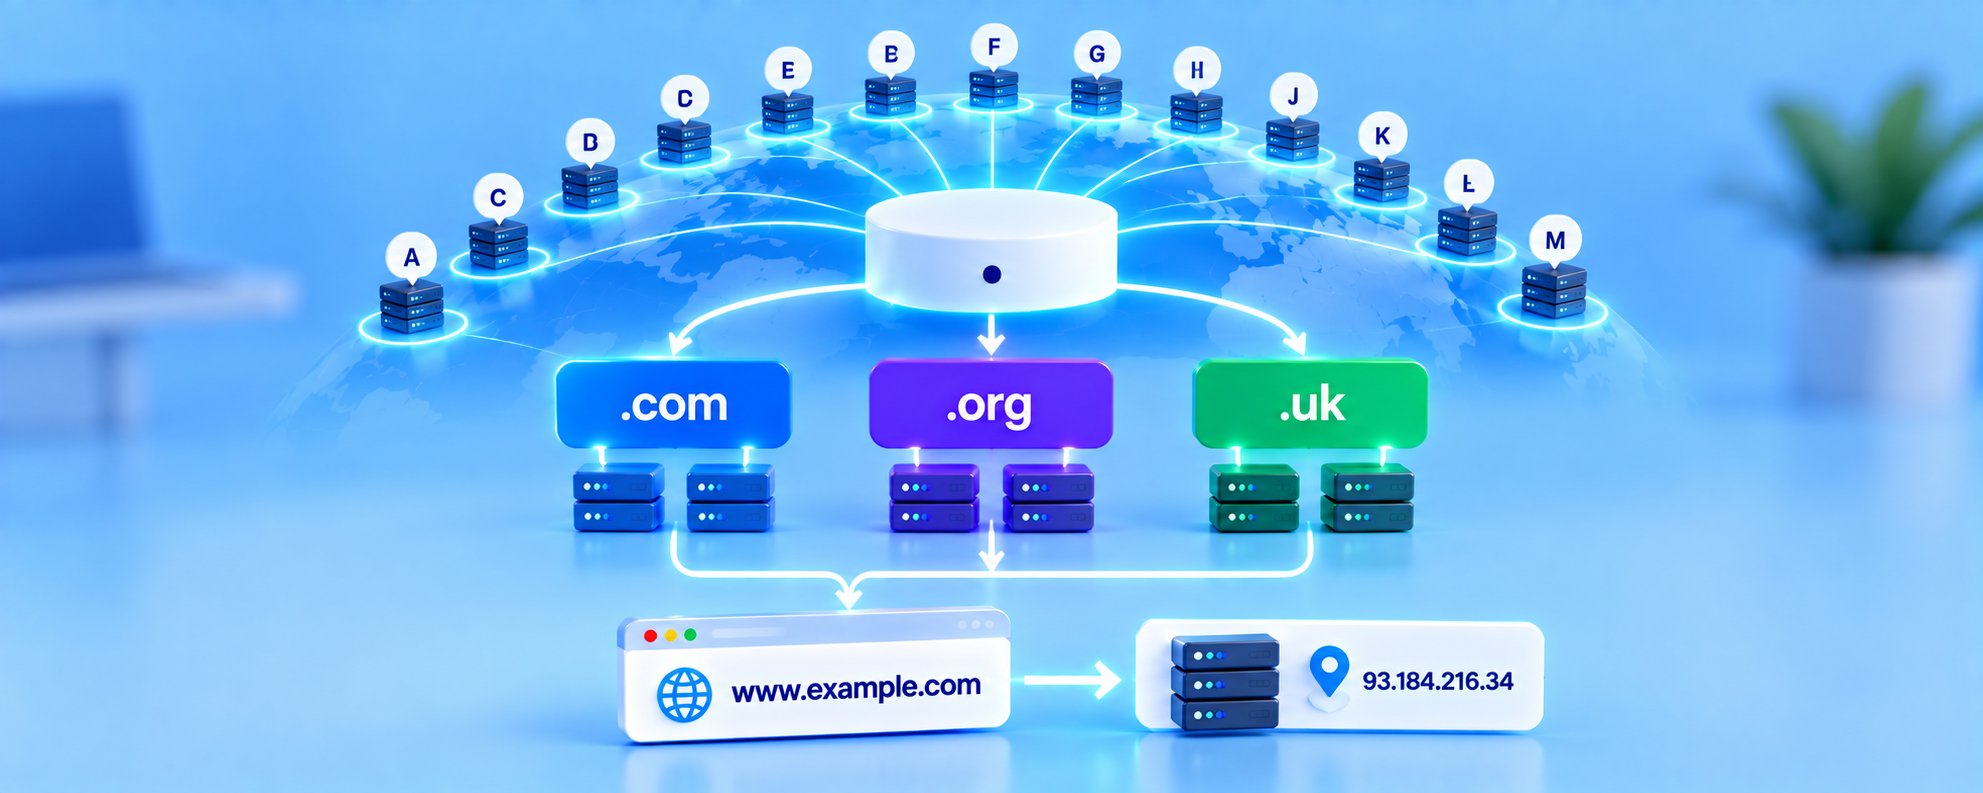
The DNS root zone is the top of DNS hierarchy, listing every TLD's nameservers. It's hosted on 13 named root server identities (A-M), which Anycast routing expands into over 2,000 physical instances worldwide. IANA maintains the file; the root has never suffered a complete outage, even under major DDoS attacks.
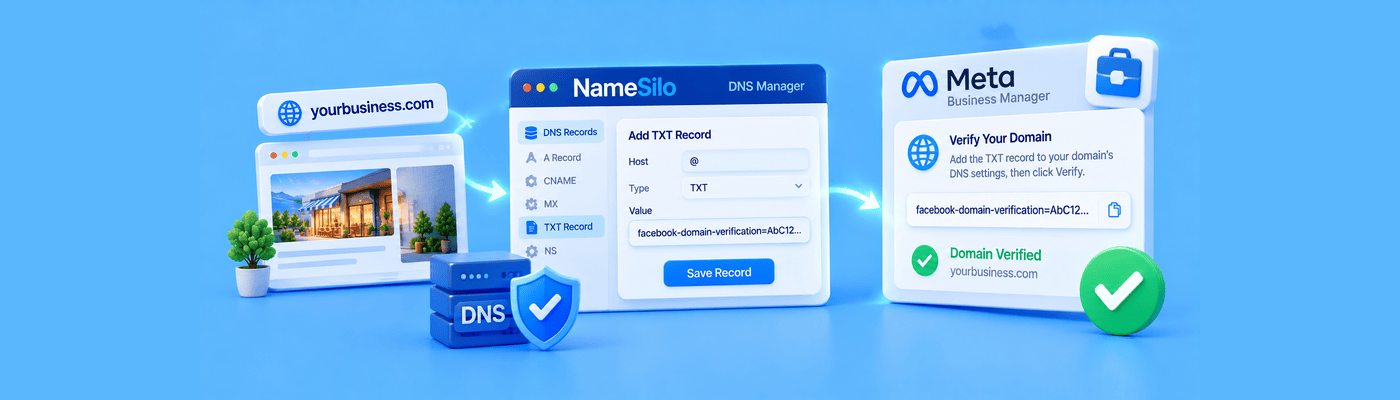
Learn how to verify domain ownership for Meta Business Manager using a DNS TXT record, HTML file, or meta tag, with NameSilo DNS setup steps.
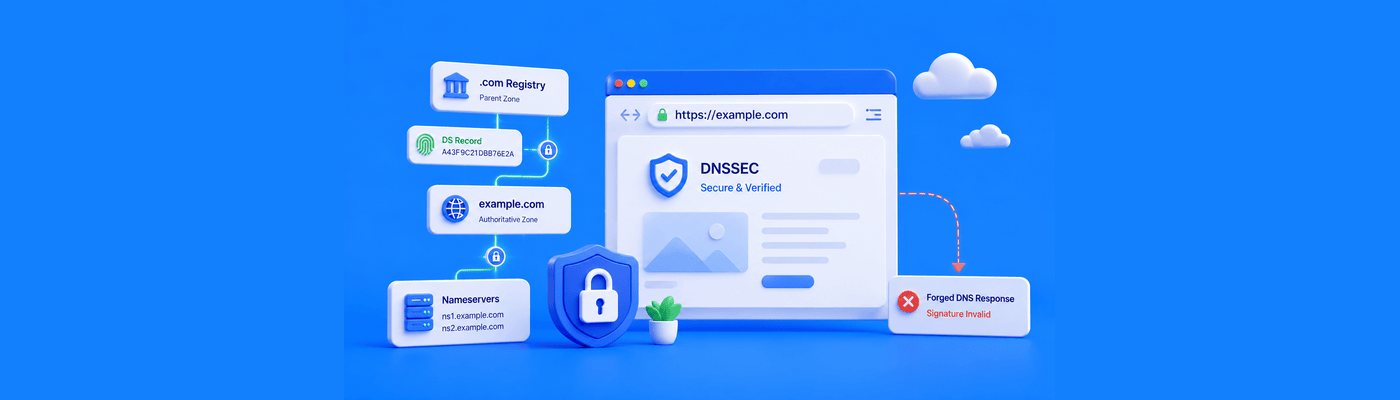
A DS record at the parent registry authenticates your domain's DNSSEC key, establishing a chain of trust that stops cache poisoning and MITM attacks. Golden rule: always remove the DS record before changing nameservers or DNS hosts, or every validating resolver returns SERVFAIL and your domain disappears.
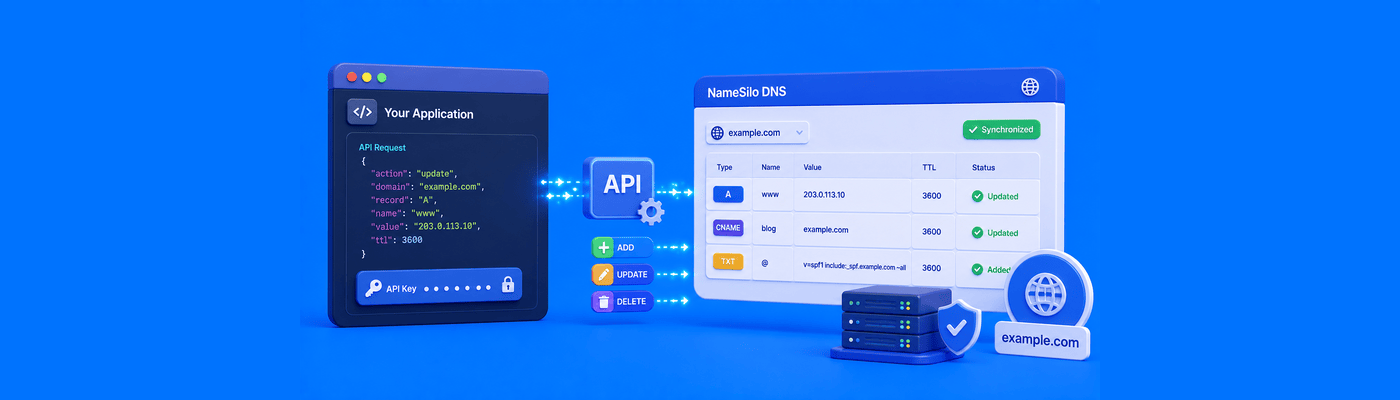
Automate DNS management with NameSilo's API using dnsListRecords, dnsAddRecord, dnsUpdateRecord, and dnsDeleteRecord. Always call dnsListRecords first to retrieve the record_id before updating or deleting; note it's passed back as rrid in update and delete calls. Useful for DDNS and Let's Encrypt wildcard verification.
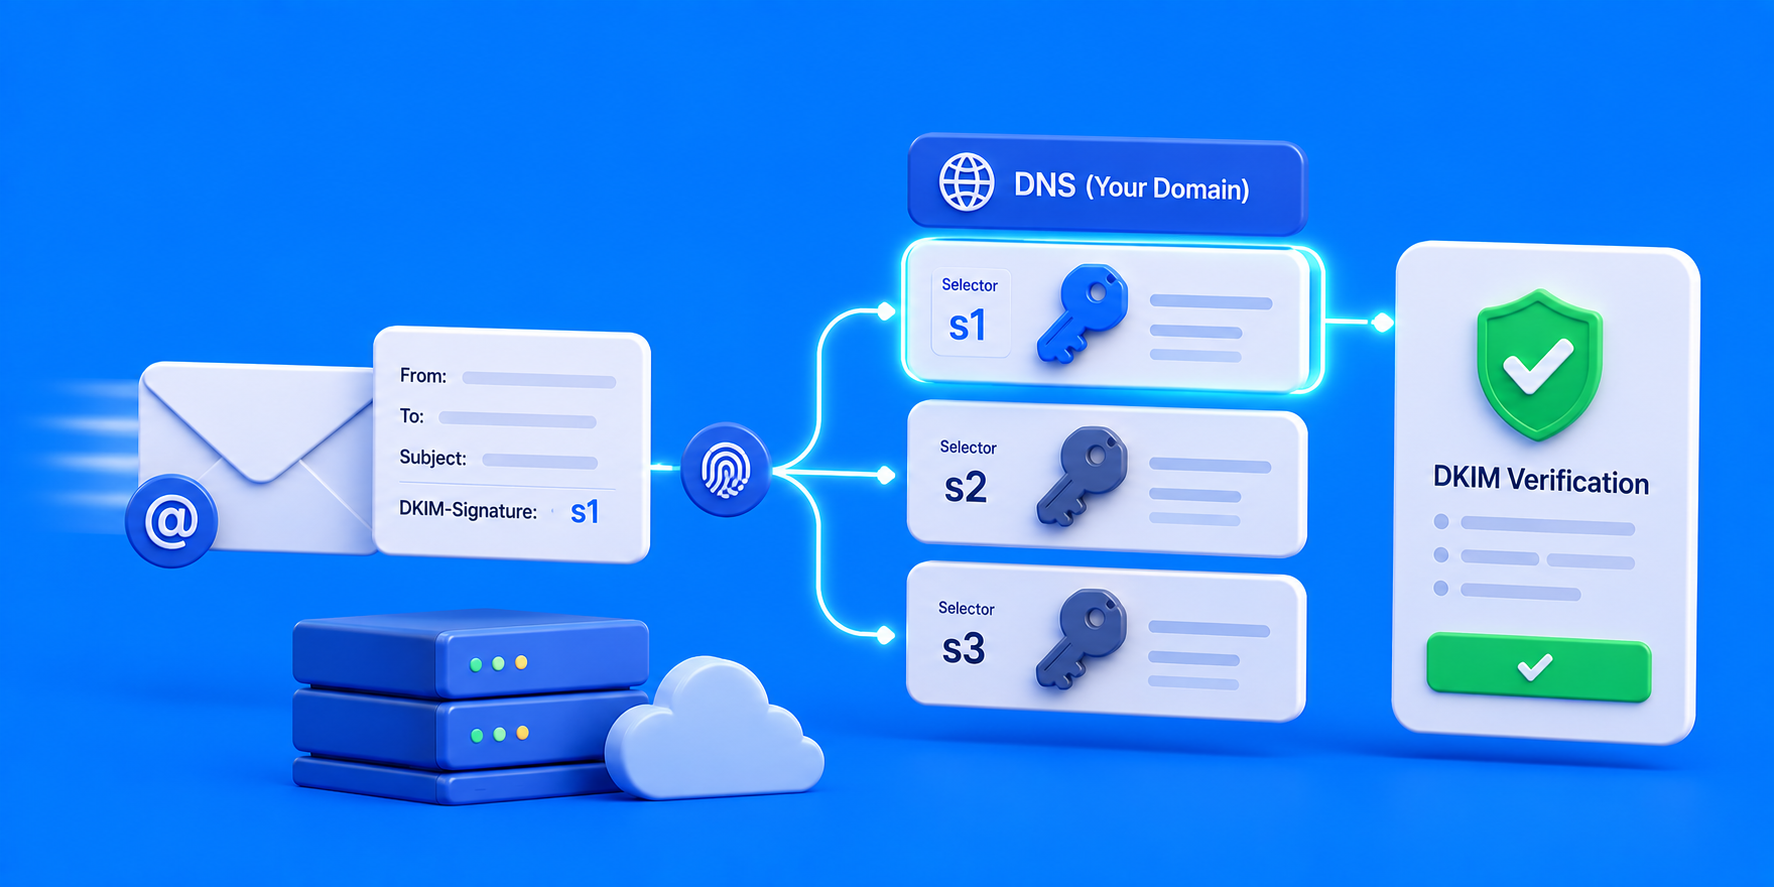
A DKIM selector identifies which public key to check in DNS, following the format selector._domainkey.yourdomain.com. Find it in your provider's admin console (Google Workspace defaults to "google"; Titan Mail shows it under Email Reputation) or by inspecting the s= tag in a raw email header.
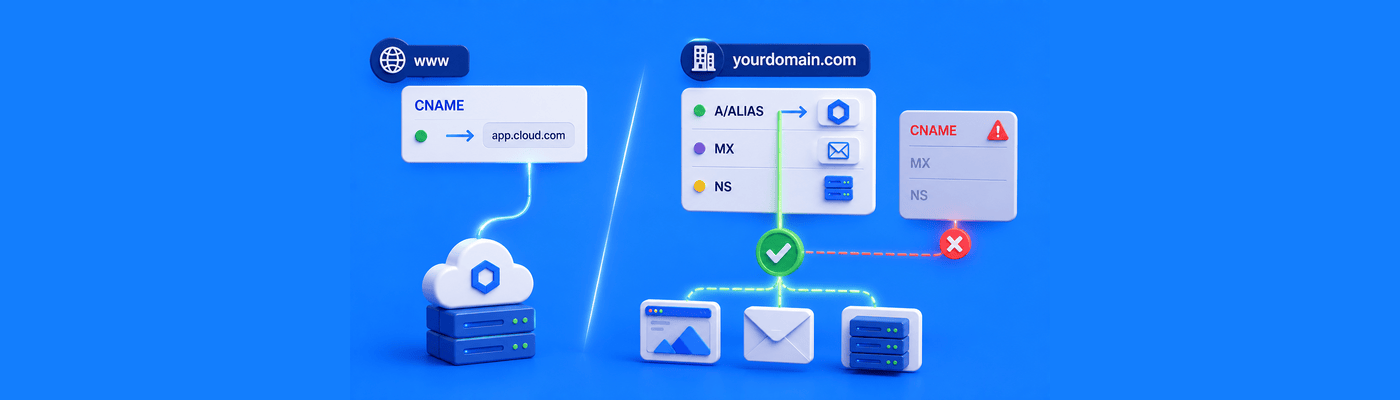
RFC 1035 forbids CNAME records at a root domain because they conflict with MX and NS records. ALIAS, ANAME, and CNAME flattening are vendor-specific workarounds, not a DNS standard. NameSilo doesn't currently offer ALIAS/ANAME; use CNAME on www plus root forwarding, or delegate DNS to a provider like Cloudflare that supports it.
A redirect chain (A > B > C) wastes crawl budget and slows load times. Googlebot abandons chains after roughly 10 hops. The most common cause is HTTP to HTTPS to WWW stacking. Fix by flattening .htaccess or Nginx rules into a single 301 redirect straight to the final URL.
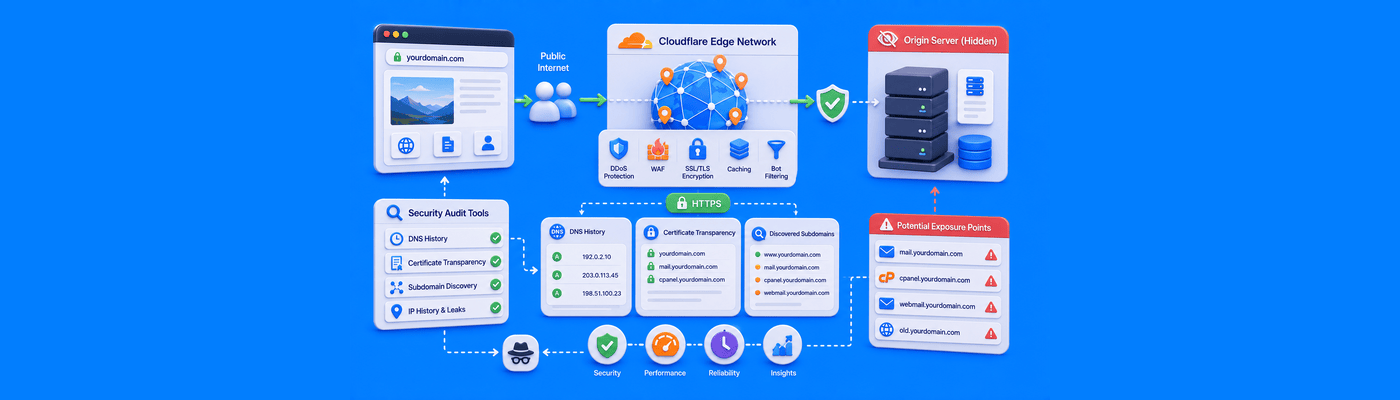
Audit your own Cloudflare setup for origin IP exposure: unprotected MX and subdomains, historical DNS records, and certificate transparency logs. Enabling the orange cloud alone does not erase a previously public IP. Lock the origin firewall to Cloudflare's IP ranges to close the gap.