DNS3 min
What is the DNS Root Zone and How Does It Work?
NS
NameSilo Staff10/1/2026
Share
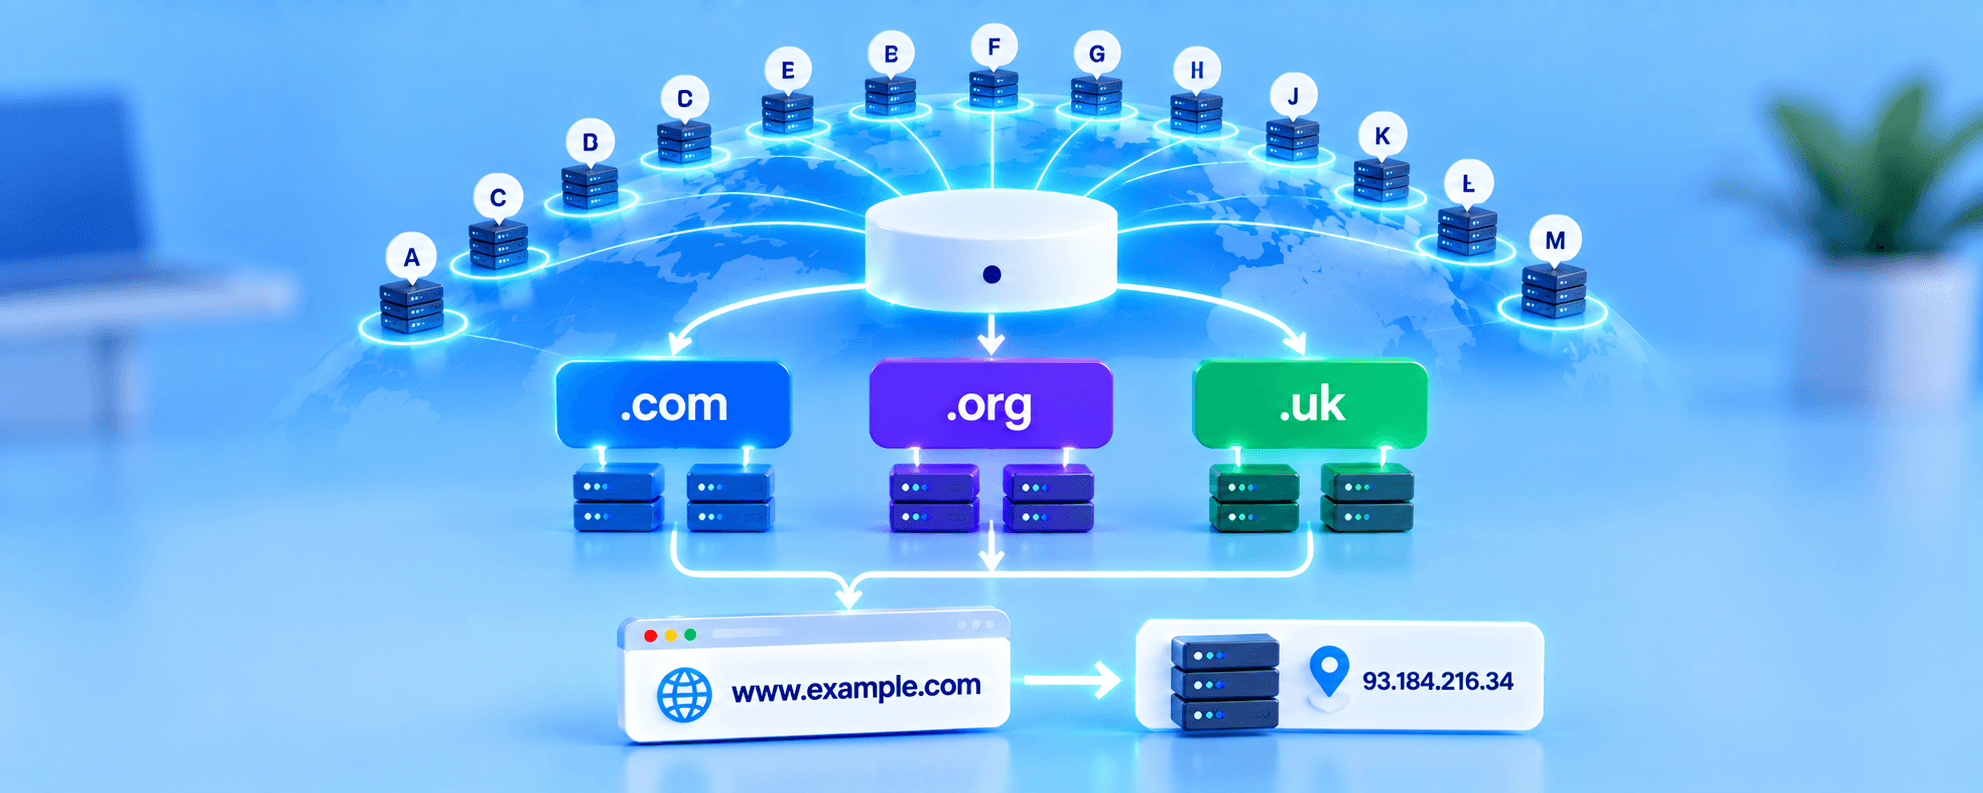
The DNS Root Zone is the absolute top level of the internet's Domain Name System hierarchy. It contains the authoritative lists of nameservers for all Top-Level Domains (like .com, .org, and .uk). Managed by ICANN, it is hosted on 13 logical root server clusters globally, directing resolving servers to the correct TLD registry to find specific websites.
The Silent Dot
Every fully qualified domain name technically ends in an invisible trailing dot: www.example.com. That final dot represents the root zone itself, the unnamed top of the entire DNS hierarchy that every other lookup descends from. Browsers hide it, but it's there in every query your device makes.
The 13 Logical Root Servers (A through M)
There are exactly 13 named root server identities, lettered A through M, operated by 12 organizations (Verisign alone runs two, A-root and J-root; every other operator runs exactly one). The number 13 traces back to a genuinely old technical constraint: the original 512-byte limit on UDP DNS responses meant only so many server addresses could fit in a single reply. That ceiling was set decades ago and has simply never needed to change.
Here's the fascinating part: those 13 identities aren't 13 physical machines. Anycast routing lets each single IP address be simultaneously announced from many physical locations worldwide, with the nearest one automatically answering any given query. As of mid-2026, those 13 identities are backed by over 2,000 operational server instances across the globe, and the distribution is intentionally uneven: some operators run hundreds of instances in regions with historically sparse DNS infrastructure, while others run just a handful.
The Role of IANA and ICANN
IANA (Internet Assigned Numbers Authority), a function of ICANN, maintains the master root zone file, the authoritative list mapping every valid TLD to its nameservers. Verisign generates and distributes that file to all 13 root server operators. The file itself is cryptographically signed via DNSSEC, and updates go through a formal, carefully governed change process before ever reaching the public root.
The Lookup Process
When your resolver doesn't already have a cached answer, it queries a root server first. The root server doesn't know your final destination, it simply points the resolver to the correct TLD server (for .com, .org, etc.). That TLD server then points to your domain's specific authoritative nameserver, which finally returns the actual IP address.
Common Mistakes
Assuming a root server outage would take down the internet: It wouldn't, and it never has. The root server system has never suffered a complete outage in its history, even during major DDoS attacks generating millions of queries per second. Anycast redundancy absorbs the load by rerouting to healthy instances, and most resolvers cache root responses anyway, meaning the average user would never notice a temporary disruption at the root level.
What This Means for You
NameSilo's authoritative nameservers integrate directly into this global chain, correctly responding once a TLD server points a resolver their way. Manage your domain's nameserver configuration through NameServer Manager, or search available names to register a new domain today.
Frequently Asked Questions
What is the DNS root zone?
The top-level authoritative file mapping every TLD to its nameservers.
How many DNS root servers are there?
13 named identities, backed by thousands of physical instances via Anycast.
Who controls the DNS root servers?
12 independent organizations, coordinated under IANA and ICANN oversight.
What does ICANN do for the internet?
Oversees the root zone, TLD policy, and global domain name governance.
What is an authoritative nameserver?
The server holding the definitive DNS records for a specific domain.
How does a DNS lookup work?
Root server, then TLD server, then authoritative nameserver, in sequence.
What happens if the DNS root servers go down?
Little to nothing; Anycast redundancy and caching prevent any single failure.
How do NameSilo nameservers communicate with the root zone?
Indirectly, by being correctly registered at the TLD level the root zone points to.

NameSilo StaffThe NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.
More articleswritten by NameSilo