DNS4 min
What is a DNS Amplification Attack? (DDoS Reflection)
NS
NameSilo Staff10/8/2026
Share
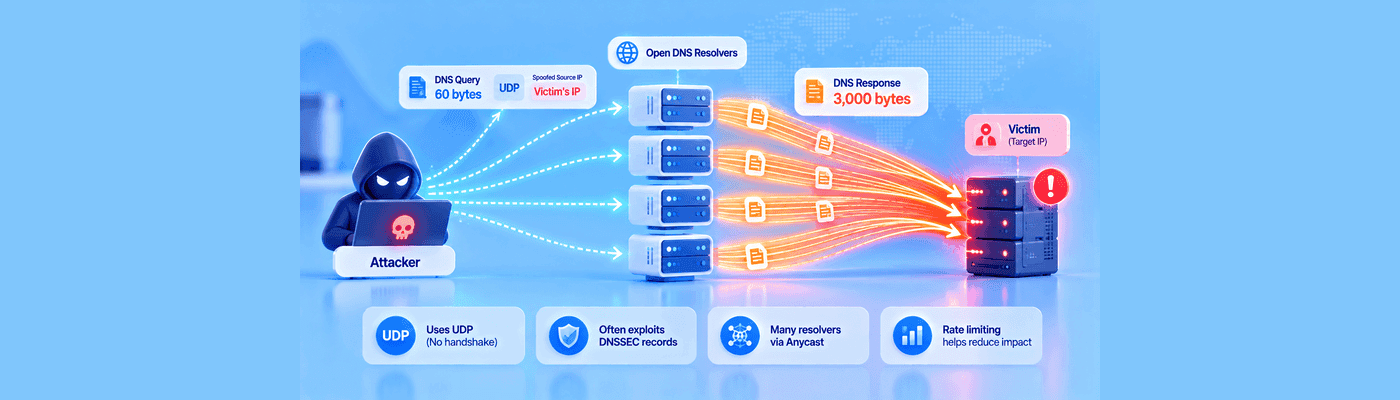
A DNS amplification attack is a volumetric Distributed Denial of Service (DDoS) attack that exploits open DNS resolvers. Attackers send small lookup requests with forged (spoofed) source IP addresses belonging to the victim. The DNS servers reply with massive response packets directed straight at the victim's server, overwhelming its network bandwidth.
The Physics of Reflection
Reflection attacks exploit a simple asymmetry: a tiny request can trigger a disproportionately massive response. The attacker never sends traffic directly at the victim, instead, they trick a third-party server into doing it for them, at a scale their own bandwidth could never achieve alone. Thousands of these reflected responses converging on one target simultaneously produce multi-hundred-gigabit floods from a comparatively modest attacking botnet.
Why DNS Is Vulnerable
DNS traditionally runs over UDP, a stateless protocol with no handshake step. TCP connections verify both sides are real before exchanging data; UDP does not. A DNS server has no built-in way to confirm the source IP on an incoming request is genuine, it simply replies to whatever address the packet claims to be from. An attacker exploits this by forging the victim's IP as the source, and the DNS server sends its response there instead of back to the real requester.
The Amplification Factor: EDNS0 Mechanics
The original DNS specification capped UDP responses at 512 bytes. EDNS0 (Extension Mechanisms for DNS) changed that, allowing servers to advertise support for much larger UDP buffer sizes, commonly up to 4096 bytes.
This extension was designed for legitimate purposes, mainly supporting DNSSEC, whose cryptographic signature records (RRSIG, DNSKEY, DS) are too large to fit in the old 512-byte ceiling. But it also handed attackers a bigger lever: a single spoofed query for an ANY record, a large TXT record, or DNSSEC-signed data can now trigger a response many times its own size.
A real-world example: a roughly 60-byte spoofed request can return a 3,000-byte response, an amplification factor near 50x. Send that query through thousands of open resolvers simultaneously, and a botnet with modest actual bandwidth can generate a flood measured in hundreds of gigabits per second.
The Role of Open Resolvers
An open resolver is a recursive DNS server configured to answer queries from anyone on the internet, not just its intended local user base. Misconfiguration, rather than malicious intent, is almost always the cause; an administrator leaves recursion open by default and never restricts it. Attackers scan the internet continuously for these misconfigured servers, building lists of reflector nodes ready to weaponize on demand.
Mitigation and Server Defense
Response Rate Limiting (RRL): Caps how many responses a DNS server sends to any single IP within a given window, throttling abuse without blocking legitimate traffic entirely.
Closing open recursion: Restricting a resolver to answer only trusted, local clients removes it from the pool of usable reflectors.
Upstream scrubbing: Routing traffic through a distributed network of redundant servers absorbs and disperses attack volume before it reaches the origin server.
What This Means for You
NameSilo's Premium DNS, powered by NuSEC, runs on a global Anycast network that distributes attack traffic across multiple geographic nodes rather than letting it concentrate on a single server. A hidden master architecture keeps your actual authoritative DNS server isolated from public queries entirely, so attackers targeting the visible Anycast nodes never reach the real configuration behind them. If a node does go down, automatic failover shifts traffic to a healthy backup within minutes, based on health checks running every 30-60 seconds.
Since NameSilo's default free nameservers don't yet support DNSSEC signing, domains needing that specific protection today can pair a third-party signing DNS host with DS records added at NameSilo. Ready to secure a new domain? Search available names.
Frequently Asked Questions
What is a DNS amplification attack?
A DDoS technique using spoofed requests to trigger massive reflected responses at a victim.
What is the amplification factor in DNS reflection?
The ratio of response size to request size, often 50x or higher with EDNS0.
Why do attackers use UDP for DNS DDoS?
UDP has no handshake, letting attackers spoof the victim's IP as the source.
What is an open DNS resolver?
A misconfigured recursive server answering queries from any public source.
How do you stop a DNS amplification attack?
Response Rate Limiting, closing open recursion, and upstream traffic scrubbing.
What is Response Rate Limiting (RRL)?
A server setting capping how many responses go to one IP in a given window.
Can an authoritative nameserver be used for amplification?
Rarely at the same scale; open recursive resolvers are the primary risk.
Does NameSilo protect against DNS DDoS attacks?
Premium DNS's Anycast network and hidden master architecture help absorb and isolate attacks.

NameSilo StaffThe NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.
More articleswritten by NameSilo