
Firewall at the Edge: Why DNS-Based Blocking Is the New Standard in Threat Defense
For years, cybersecurity focused on defending the endpoint: firewalls, antivirus software, and application-level filters. But as threats have grown more sophisticated and more decentralized, the security industry has shifted its attention to a new front line: the Domain Name System (DNS).
In 2025, DNS-based blocking is quickly becoming a foundational layer in modern threat defense. Why? Because DNS sits at the center of almost every online interaction. Before a malicious site can be loaded, before malware can call home, and before phishing pages can steal credentials, DNS must first resolve the destination.
This article explores how DNS-based firewalls work, why they’re effective, and why businesses, developers, and even individuals are adopting them as a first-layer defense system. We’ll also explore how NameSilo’s DNS infrastructure supports secure, policy-based resolution without compromising speed or control.
What Is DNS-Based Blocking?
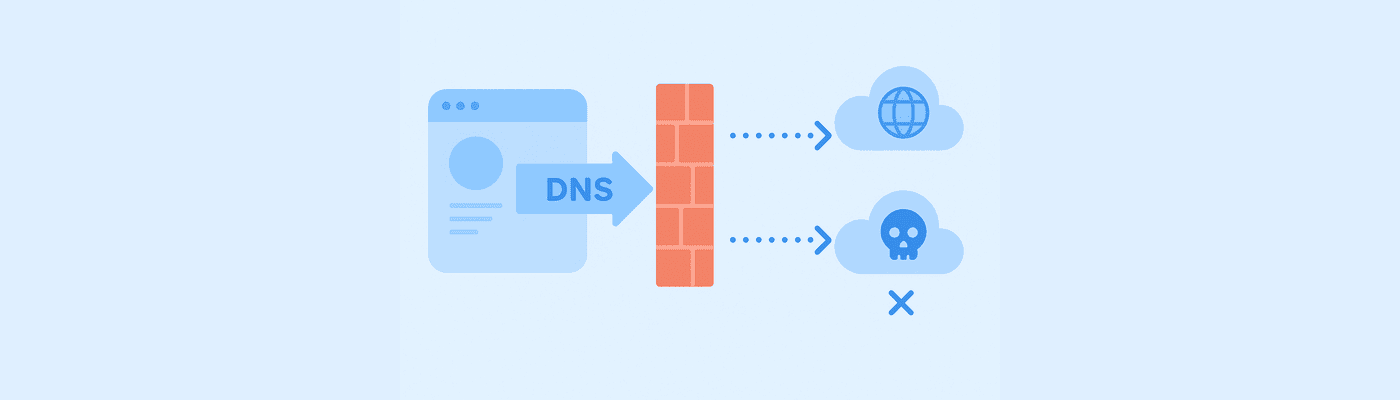
DNS-based blocking, also known as DNS firewalling, is the practice of intercepting DNS queries and preventing the resolution of known malicious or unwanted domains. Instead of allowing a device to connect to a flagged IP, the DNS resolver simply responds with a null or redirect response, effectively blocking the threat at the lookup stage.
Unlike traditional firewalls that analyze traffic at the network or transport layer, DNS firewalls operate at the domain name resolution layer, making them faster, lighter, and more proactive.
Why DNS Is the Perfect Security Layer
1. Every Online Action Starts with DNS
Whether you're visiting a website, clicking a link in an email, or launching a mobile app, the first step is typically a DNS lookup. That makes it an ideal place to intercept malicious intent early.
2. It’s Lightweight and Fast
DNS lookups are low-bandwidth and low-latency, making filtering efficient without slowing down network performance.
3. It’s Universal
DNS is used across all platforms, devices, and operating systems. Implementing a DNS firewall protects everything from mobile phones to smart TVs to enterprise servers.
4. It’s Non-Invasive
Unlike deep packet inspection or SSL interception, DNS-based blocking doesn’t compromise user privacy. It stops threats without decrypting traffic.
How DNS Firewalls Work
When a user tries to visit a website, their device queries a recursive DNS resolver (often provided by a DNS service like Cloudflare, Google DNS, or NameSilo). A DNS firewall steps in by:
- Checking the domain against a real-time threat database
- If the domain is safe, the request proceeds as normal
- If the domain is malicious or unapproved, the request is blocked or redirected to a safe landing page
The beauty of this approach is that it works before any connection is made, stopping phishing, ransomware, malware C2 (command & control), and domain-based data exfiltration.
Use Cases: Who Should Use DNS-Based Blocking?
1. Small Businesses Without Full IT Teams
Implementing endpoint firewalls and antivirus across every device can be complex and expensive. A DNS firewall protects the entire network with minimal setup.
2. Remote Workforces and Hybrid Offices
DNS firewalls can protect devices outside the corporate perimeter, especially when combined with secure resolvers or VPN-based DNS tunneling.
3. Parents and Schools
DNS filtering is a simple way to restrict adult content, social media, or gaming domains on shared or public devices.
4. Developers and Sysadmins
Secure DNS policies can prevent malware callbacks or third-party services from communicating with banned or deprecated domains.
Benefits Over Traditional Firewalls
Traditional firewalls operate at the packet level and are often resource-intensive. They may interfere with encrypted traffic and are harder to deploy across remote or diverse device environments. In contrast, DNS-based blocking works at the domain level, is lightweight and fast, respects end-to-end encryption, and functions across any network-connected device with minimal configuration.
DNS-based firewalls are not meant to replace traditional firewalls but to complement them, providing security coverage earlier in the connection chain.
Threats DNS Blocking Can Prevent
- Phishing attempts: Block domains used in email scams
- Malware downloads: Prevent the resolution of known delivery servers
- C2 callouts: Stop infected machines from communicating with attackers
- Crypto-mining scripts: Block domains associated with in-browser mining
- Typosquatting and lookalike domains: Prevent users from accidentally visiting imposter websites
Implementing DNS Firewalling with NameSilo
While NameSilo provides secure DNS management and supports DNSSEC by default, advanced users can layer in DNS firewalling by:
- Using DNS filtering services like Quad9 or NextDNS for recursive resolution
- Managing allow/block lists through local DNS resolvers or cloud platforms
- Setting TTL (time to live) values to manage how long a block is enforced
- Using API-based control (NameSilo’s API allows programmatic DNS management and record changes)
For enterprise users or resellers managing multiple domains, DNS firewalling can also be integrated into your larger security orchestration.
DNSSEC vs. DNS Firewall: What’s the Difference?
While both operate at the DNS level, they serve different purposes:
- DNSSEC: Authenticates DNS records to ensure they haven’t been tampered with. It’s about integrity.
- DNS Firewall: Filters DNS queries based on threat intelligence. It’s about access control.
Using both together offers layered security.
What to Watch Out For
1. False Positives
DNS blacklists may occasionally block legitimate domains. Use customizable lists or allowlist overrides.
2. Lack of Logging
Basic DNS services may not offer query logging. For forensic analysis or compliance, use services that support detailed logging or integrate with SIEM tools.
3. Over-Reliance
DNS blocking is powerful, but it’s not a silver bullet. Combine it with endpoint protection, SSL, and good user training.
Looking Ahead: The Rise of Edge-Based DNS Security
As edge computing and remote access become more common, DNS-based blocking will grow even more essential. Expect to see:
- AI-enhanced DNS firewalls that adapt to new threats in real time
- Custom blocklists per user or device
- DNS-layer content filtering for productivity enforcement
This model aligns perfectly with zero-trust architecture, pushing security closer to the point of origin: the user and their device.
Conclusion
In today’s threat landscape, reacting isn’t enough. DNS-based blocking lets you intercept attacks before they even begin, turning a fundamental part of the internet into a powerful security layer.
Whether you're a business owner, parent, sysadmin, or developer, understanding and implementing DNS-level protection is no longer optional; it’s the new standard.
NameSilo helps you secure your domain infrastructure from the ground up. With DNSSEC support, reliable DNS management, and powerful API access, you're empowered to integrate DNS-layer security with ease. Whether you're managing one site or a hundred, NameSilo puts you in control of your domain security.
NameSilo Staff
The NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.


