How to Protect Your Domain Name from Employee Theft
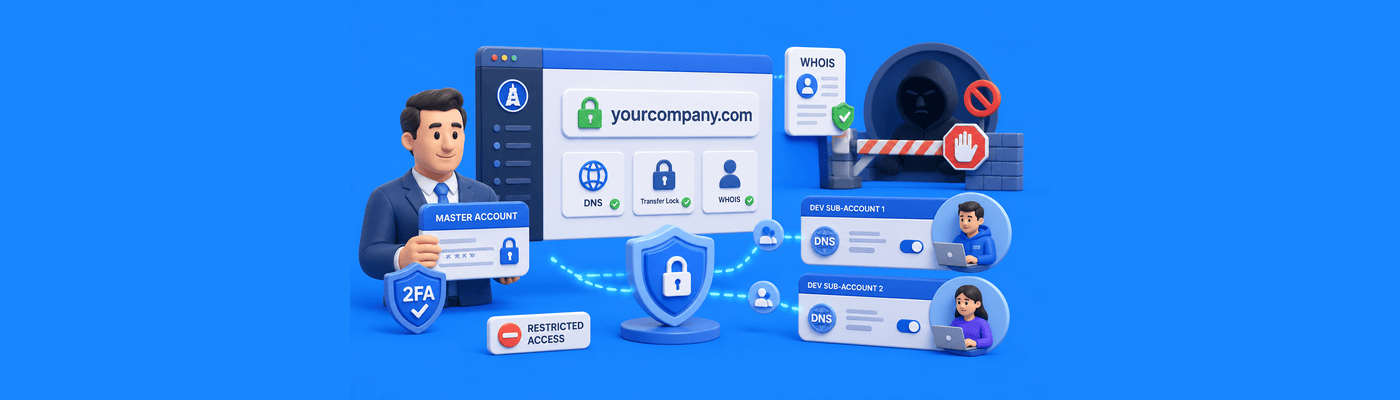
To protect your domain name from employee theft, never share your primary registrar login credentials. Instead, ensure the domain's legal WHOIS registrant data is in the company's name, not an employee's. Use registrar Sub-Accounts to grant IT staff restricted, "manage-only" access to DNS records while locking their ability to transfer or sell the domain.
Technical Access vs Legal Ownership
First, understand that you don't truly "own" a domain, you lease registration rights from a registry. ICANN and registries maintain ultimate authority. What you control is the registration, and two separate concepts govern that control:
Access Type | What It Controls | Who Should Have It |
DNS access | Website/email routing | IT staff, developers, agencies |
Registrant ownership | Legal registration rights | Company executives only |
DNS access: Ability to modify A records, MX records, nameservers. Technical but not ownership.
Registrant control: The WHOIS registrant holds registration rights. Whoever controls this can transfer, sell, or let the domain expire.
The mistake: Companies give full account access when employees only need DNS access. This exposes registration controls unnecessarily.
The Threat Model: Insider Domain Theft
How it happens:
- Employee has full registrar account access
- Employee changes WHOIS registrant to their personal name
- Employee unlocks domain and initiates transfer
- Employee accepts transfer at new registrar
- Company loses domain permanently
Timeline: This can happen in under 24 hours. By the time you notice, the domain is gone.
Recovery difficulty: Without documentation proving corporate ownership, recovery requires expensive legal action.
Common triggers: Termination disputes, unpaid contractors, agency relationship breakdowns.
Decision Framework: Master vs Sub-Accounts
Account Type | Access Level | Use Case |
Master account | Full control | Founders, C-suite only |
Sub-account (Full) | Most features | Senior IT management |
Sub-account (Limited) | DNS only | Developers, agencies |
Role-Based Access Control (RBAC): The principle is simple, grant minimum necessary permissions.
Developers need: DNS record management, SSL configuration.
Developers don't need: Transfer authority, WHOIS editing, account billing.
Never share master credentials. Create sub-accounts with specific permissions instead.
Implementation Steps: Secure Your Domain
Step 1: Audit WHOIS registrant data, verify it's corporate, not a former employee's personal info.
Step 2: Use corporate email ([email protected]) for the master account, not personal Gmail.
Step 3: Enable two-factor authentication with an authenticator app.
Step 4: Create sub-accounts in NameSilo's Sub-Account Manager for each team member or agency.
Step 5: Assign minimum permissions, DNS management only. Restrict transfer and WHOIS editing.
Step 6: Keep clientTransferProhibited enabled. Only unlock when you personally initiate a transfer.
Step 7: Document ownership with registration receipts and WHOIS history.
Step 8: Revoke sub-accounts for departed employees immediately. Audit quarterly.
Common Mistakes
Shared Gmail credentials: Multiple employees sharing one generic Gmail account for domain registration. When someone leaves, they still have access.
Registering under personal names: An IT manager registers domains under their own name "for convenience." They leave. The domain is legally theirs.
Agency ownership: Your web agency registered the domain "on your behalf" but under their account. You don't own it, they do.
No 2FA: Without two-factor authentication, a compromised password means total account loss.
Forgetting to revoke access: Former employees retain sub-account access months after termination.
What This Means for You
NameSilo's Sub-Account Manager provides granular permission controls. Give developers DNS access without exposing ownership functions.
Need a new domain? Register it properly under your company name from day one.
Frequently Asked Questions
Who legally owns a company domain name?
The WHOIS registrant, ensure it's your company.
How do I give my developer access to my domain?
Create a sub-account with DNS-only permissions.
What happens if an employee steals my domain?
Legal action required. Prevention is easier than recovery.
Can I lock a domain from being transferred?
Yes. Enable clientTransferProhibited status.
What is a registrar sub-account?
Restricted login with limited permissions you define.
Should my web agency own my domain?
Never. Register under your company's account.
How do I secure my NameSilo account?
Enable 2FA, use corporate email, create sub-accounts.
What is domain hijacking?
Unauthorized transfer of ownership to another party.
NameSilo Staff
The NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.