
What is DNSSEC and Do You Need It
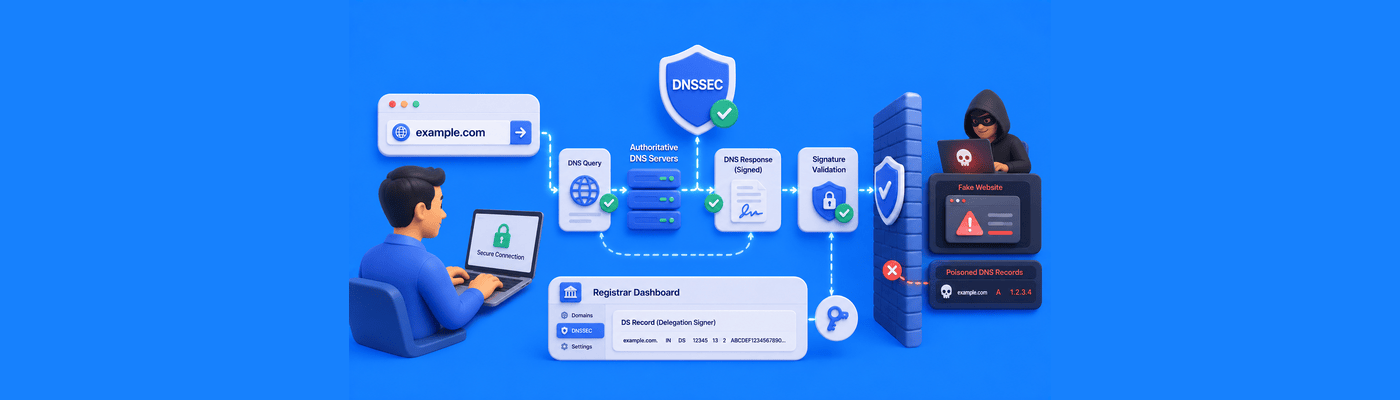
DNSSEC (Domain Name System Security Extensions) is a security protocol that adds cryptographic signatures to your DNS records. It prevents DNS spoofing and cache poisoning by ensuring that when a user types your domain name, they are routed to your actual server and not secretly redirected to a hacker's fake website.
The Vulnerability of Standard DNS
Standard DNS has no identity verification. When a browser asks "what IP address is example.com?", the resolver returns an answer without confirming whether that answer was tampered with.
Cache poisoning: An attacker injects false DNS records into a resolver's cache. Every user querying that resolver gets directed to the attacker's server instead of yours.
DNS spoofing: A fraudulent DNS response routes traffic to a malicious server in real time.
Both attacks are invisible to the end user. The URL bar shows the correct domain. The page looks identical. The user logs in and the attacker harvests credentials.
DNSSEC closes this vulnerability by cryptographically signing every DNS response, allowing resolvers to verify authenticity.
Why It Matters: Man-in-the-Middle Attacks
Without DNSSEC, an attacker can create an exact replica of your website, redirect DNS traffic to it, and collect passwords and payment details from real customers.
High-value targets: Banks, e-commerce stores, healthcare portals, and any site handling authentication are primary targets.
The scale: A single poisoned resolver can redirect millions of users before detection. DNSSEC validates signatures at every step of the DNS chain, making poisoned responses cryptographically invalid.
Decision Framework: Who Needs DNSSEC?
Use Case | DNSSEC Needed? | Reason |
Bank, e-commerce, SaaS login | Yes | High credential theft risk |
Business with customer data | Yes | Compliance and trust |
Government or healthcare | Yes | Regulatory requirement |
Marketing or blog site | Optional | Lower attack value |
Personal portfolio | Low priority | Setup complexity outweighs risk |
The honest assessment: For low-traffic personal sites, the configuration complexity and migration risk often outweigh the security benefit. For any site handling logins, payments, or sensitive data, DNSSEC should be considered a baseline requirement.
Implementation Steps: Enable DNSSEC
DNSSEC requires coordination between your DNS provider and your domain registrar.
Step 1: Confirm your DNS provider supports DNSSEC signing.
Note: NameSilo's default nameservers (ns1/ns2/ns3.dnsowl.com) do not currently support DNSSEC signing, though an upgrade is planned. If you need DNSSEC now, use a third-party DNS provider such as Cloudflare or Route 53.
Step 2: Enable DNSSEC signing at your DNS provider. They will generate a DS (Delegation Signer) record containing your zone's public key fingerprint.
Step 3: Copy the DS record values: Key Tag, Algorithm, Digest Type, and Digest.
Step 4: In NameSilo's domain manager, navigate to DS Records and add the DS record provided by your DNS host.
Step 5: Allow 24-48 hours for propagation. Verify with a DNSSEC lookup tool such as dnsviz.net.
Common Mistakes
Migrating DNS or changing nameservers without disabling DNSSEC first: This is the most critical DNSSEC mistake. When you move to a new DNS host, the DS record at the registrar still points to the old provider's key. The cryptographic chain breaks instantly. Every resolver that enforces DNSSEC validation refuses to resolve your domain and your site goes offline globally.
The correct procedure: Disable DNSSEC at the registrar, remove the DS record, complete the migration, then re-enable with the new provider's DS record.
Forgetting to renew DS records: DNSSEC keys expire. A missed key rollover breaks the chain identically to a migration error.
What This Means for You
NameSilo's DS Records panel supports full DNSSEC management for domains using external DNS providers. If you need a domain to protect with DNSSEC, search available names at NameSilo.
Frequently Asked Questions
What does DNSSEC protect against?
DNS spoofing and cache poisoning attacks.
Is DNSSEC necessary for a website?
Essential for financial and login sites; optional for personal blogs.
How does DNS spoofing work?
Attacker injects false DNS records, redirecting users to a malicious server.
What happens if DNSSEC is misconfigured?
Resolvers reject your domain and the site goes offline globally.
How do I turn on DNSSEC?
Enable at DNS provider, then add the DS record at your registrar.
What is a DS record?
A Delegation Signer record with your zone's public key fingerprint.
Does DNSSEC encrypt my website traffic?
No. It authenticates DNS only. SSL handles traffic encryption.
Does NameSilo support DNSSEC?
DS record management is supported. Default nameservers do not yet sign zones; upgrade planned.
NameSilo Staff
The NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.


