Privacy & Security4 min
How to Use WHOIS Privacy for GDPR Compliance
NS
NameSilo Staff9/23/2026
Share
This article is for educational purposes only and does not constitute legal advice. Consult a qualified attorney for compliance guidance specific to your business.
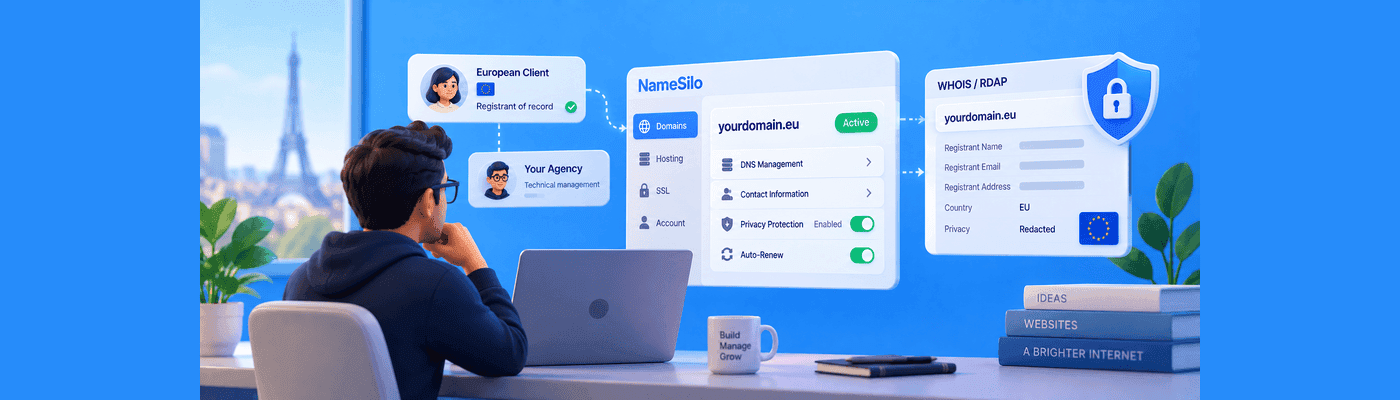
If you're an agency registering domains for European clients, GDPR compliance starts with getting the registrant relationship right, then ensuring WHOIS Privacy is active on that registration. The client should be the registrant of record, not the agency, and WHOIS Privacy should be confirmed active regardless of who completes the registration on their behalf.
Why This Is an Agency Problem, Not Just a Client Problem
When an agency registers a domain on a client's behalf, it's tempting to use the agency's own details to move quickly, then hand over access later. This creates two separate problems.
First, it's a liability issue: if the agency is listed as registrant, the agency's own name and contact details become the publicly exposed party, and the agency inherits responsibility for a domain it doesn't actually own long-term. Second, it complicates GDPR obligations, since the actual data controller relationship gets murky when the registrant on record isn't the person the site is actually for.
The client should be the registrant. The agency's role belongs in the Administrative or Technical contact fields instead, where it can still manage DNS, renewals, and technical setup without taking on registrant-level exposure or liability.
What Is the GDPR Mandate, and How Does It Meet the Domain Registry System?
Domain registration has traditionally required listing the registrant's real name, address, email, and phone number publicly in WHOIS, the internet's public ownership directory. GDPR, effective since May 2018, directly conflicts with that open-by-default model whenever the registrant is an individual protected under the regulation, which includes many of your clients' own names if they register as individuals rather than a registered business entity.
A technical update worth knowing: ICANN formally sunset the WHOIS protocol on January 28, 2025, replacing it with RDAP (Registration Data Access Protocol). Most tools, including registrar lookup pages, still use "WHOIS" as the everyday term, but RDAP is the actual system running underneath.
Redaction, Not Substitution: What WHOIS Privacy Actually Does
WHOIS Privacy does not transfer the domain to a third party or insert an alternate identity in place of the registrant. The client's submitted name, address, and contact details remain the true registration data on file, and they remain the registrant of record throughout.
What privacy changes is visibility, not ownership. With WHOIS Privacy active, that registration data is withheld from the public WHOIS/RDAP lookup rather than displayed openly. This matters for the agency relationship too: enabling privacy doesn't give the agency any additional control or ownership, it simply keeps the client's real data out of public view.
Common Mistakes
Registering the domain under the agency's own name "for now": This is the most common compliance and liability mistake agencies make. Fix the registrant field to the client before launch, not after, since a later ownership correction is more work than doing it right at registration.
Assuming privacy is automatically enabled just because a domain is registered: Confirm it's active on the specific registration, especially when managing many client domains across different registrars.
What This Means for You
When registering on a client's behalf, set the client as registrant and confirm WHOIS Privacy is active, included free with every NameSilo domain, permanently. The agency can still hold Administrative or Technical access to manage the account. Review pricing for your client portfolio.
Frequently Asked Questions
Should my agency or my client be the domain registrant?
The client. The agency should hold Administrative or Technical contact instead.
Does GDPR apply to domain names?
Yes, whenever the registrant is an individual protected under the regulation.
How does WHOIS privacy protect my client's personal data?
It withholds their registration data from public WHOIS/RDAP display.
Does WHOIS privacy change who owns the domain?
No. The client remains registrant of record; only public visibility changes.
What if I already registered a client's domain under my agency's name?
Update the registrant contact to the client as soon as possible.
Can I manage a domain without being the registrant?
Yes, through the Administrative or Technical contact roles.
Does NameSilo charge for GDPR privacy protection?
No. WHOIS Privacy is included free with every supported domain registration.
How do I confirm privacy is active on a client's domain?
Check the domain's WHOIS Privacy status in the registrar account directly.

NameSilo StaffThe NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.
More articleswritten by NameSilo