Why Do Forwarded Emails Fail DMARC Checks?
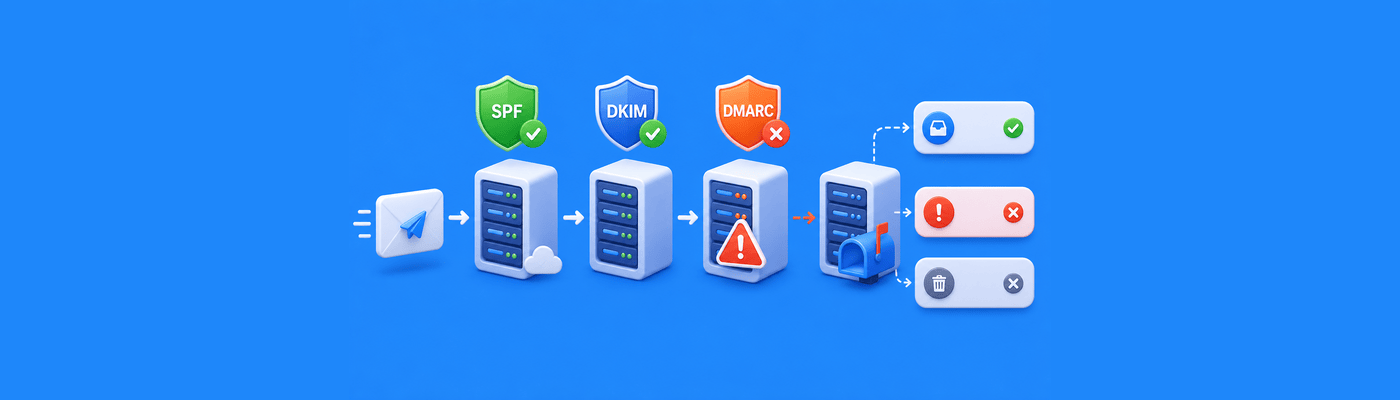
Forwarded emails often fail DMARC checks because the forwarding server changes the email’s delivery path without preserving SPF alignment. When the receiving mail server checks the sender’s SPF record, it sees the forwarding server’s IP address instead of the original sender’s server. If DKIM is missing, broken, or modified during forwarding, the message may fail DMARC entirely and get rejected or sent to spam.
Why Email Forwarding Breaks Modern Authentication
Email forwarding used to be simple. A message arrived at one mailbox and got redirected to another inbox without much security validation happening in the background.
That changed once providers like Gmail, Yahoo, Microsoft, and Apple began enforcing stricter anti-spoofing policies.
Today, email systems rely heavily on:
- SPF
- DKIM
- DMARC
These authentication methods help verify whether a message actually came from the domain it claims to represent. The problem is that forwarding interrupts part of that trust chain.
A forwarded email may still appear legitimate to a user, but technically the authentication checks can fail during transit.
This is one of the biggest reasons businesses suddenly notice:
- forwarded emails landing in spam
- missing emails
- rejected messages
- intermittent delivery failures
- DMARC quarantine notices
Understanding SPF, DKIM, and DMARC
SPF Verifies Sending Servers
SPF (Sender Policy Framework) checks whether the sending mail server is authorized to send mail for a domain.
For example:
example.com may authorize:
- Google Workspace
- Microsoft 365
- Zoho Mail
When an email arrives, the receiving server compares the sender’s IP address against the SPF record published in DNS.
If the server is not listed, SPF fails.
DKIM Verifies Message Integrity
DKIM adds a cryptographic signature to the email header.
If the message content changes during transit, the signature can fail.
DKIM is often more forwarding-friendly because forwarding servers usually do not modify the signed headers.
However:
- some forwarding systems rewrite headers
- mailing lists alter message bodies
- antivirus scanners inject content
These modifications can invalidate DKIM signatures.
DMARC Ties SPF and DKIM Together
DMARC tells receiving mail servers how to handle messages that fail authentication.
A domain owner can specify:
- none
- quarantine
- reject
Modern providers increasingly honor strict DMARC policies.
If forwarding breaks SPF and DKIM simultaneously, the message may never reach the inbox.
Why SPF Commonly Fails During Forwarding
SPF was never originally designed for email forwarding.
Here is what happens:
- Google sends an email from [email protected]
- The message arrives at forwardingdomain.com
- forwardingdomain.com forwards the message to Outlook
- Outlook checks SPF
The problem:
Outlook sees the forwarding server’s IP address, not Google’s original sending server.
The forwarding server usually is not listed in Google’s SPF record.
Result:
SPF fails.
This is the single most common reason forwarded emails fail DMARC validation.
Why DKIM Sometimes Saves Forwarded Emails
If DKIM remains intact during forwarding, DMARC can still pass even when SPF fails.
That is because DMARC only requires either:
- SPF alignment
or
- DKIM alignment
If the DKIM signature survives transit, the message may still authenticate successfully.
However, DKIM breaks more often than many people realize.
Common causes include:
- subject line modifications
- antivirus disclaimers
- mailing list footers
- MIME encoding changes
- forwarding filters altering content
Once DKIM breaks too, DMARC fails entirely.
Why Yahoo and Gmail Became Stricter
Yahoo and Gmail dramatically tightened email authentication enforcement after massive increases in:
- phishing
- spoofing
- impersonation
- business email compromise attacks
Both providers now expect domains sending moderate or high email volumes to implement:
- SPF
- DKIM
- DMARC
They also increasingly penalize forwarding setups that do not preserve authentication correctly.
This is why users often notice:
- forwarded emails suddenly failing after years of working
- delivery inconsistencies
- spam placement spikes
The forwarding system itself may not have changed.
The receiving providers simply became stricter.
Common Real-World Scenarios
Domain Forwarding to Gmail
A business forwards:
to:
Initially everything works.
Then:
- client emails disappear
- replies bounce
- invoices land in spam
The issue is often a failed SPF alignment during forwarding.
Registrar Email Forwarding
Many registrars provide simple forwarding services.
These services are convenient but may not fully support:
- ARC
- SRS
- advanced DKIM preservation
As DMARC enforcement becomes stricter, basic forwarding systems can struggle.
Mailing Lists and Newsletters
Mailing lists commonly:
- modify subject lines
- append unsubscribe footers
- rewrite headers
This frequently breaks DKIM signatures.
If SPF also fails due to forwarding, DMARC rejects the message.
What Is SRS and Why Does It Matter?
SRS stands for Sender Rewriting Scheme.
It helps forwarding servers preserve SPF alignment by rewriting the sender address during forwarding.
Instead of forwarding:
The forwarding server rewrites it into a special encoded sender format tied to the forwarding domain.
This allows SPF to validate correctly.
Without SRS:
SPF almost always fails during forwarding.
Not all forwarding systems support SRS properly.
What Is ARC?
ARC stands for Authenticated Received Chain.
ARC allows forwarding systems to preserve authentication results from earlier mail servers. Think of ARC as a trust relay. It tells downstream providers:
“This message originally passed authentication before forwarding altered it.”
Large providers increasingly rely on ARC to reduce false-positive DMARC failures.
However:
- ARC adoption is still inconsistent
- many smaller forwarding systems do not support it
- some providers ignore ARC entirely
Signs Your Forwarded Emails Are Failing DMARC
Common symptoms include:
Emails Arrive in Spam
Messages may still deliver but get classified as suspicious.
Some Providers Reject Mail Entirely
Yahoo may reject messages while Gmail accepts them.
Delivery Is Inconsistent
Some forwarded messages work while others fail.
You Receive Bounce Notices
You may see:
- SPF fail
- DMARC reject
- DKIM invalid
- policy quarantine warnings
Example rejection message:
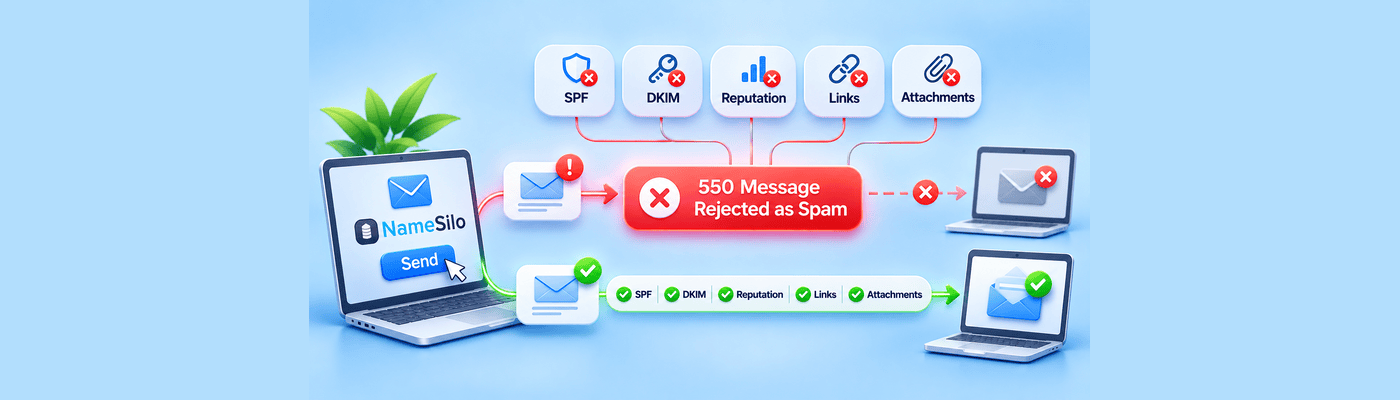
550 5.7.26 Unauthenticated email from example.com is not accepted due to domain DMARC policy.
Business Emails Suddenly Stop Arriving
This commonly happens after:
- enabling stricter DMARC policies
- switching email providers
- changing forwarding services
How to Verify DMARC Failures
Check Email Headers
Most providers allow viewing raw email headers.
Look for:
- SPF=fail
- DKIM=fail
- DMARC=fail
Use MXToolbox or Similar Tools
Tools can analyze:
- SPF records
- DKIM configuration
- DMARC policies
Check DMARC Aggregate Reports
If configured, DMARC reports show:
- authentication failures
- sending sources
- forwarding problems
- spoofing attempts
Test Using Multiple Providers
Forward emails to:
- Gmail
- Outlook
- Yahoo
- Apple Mail
Different providers enforce DMARC differently.
Quick Fix Checklist
- Enable DKIM signing on your email provider
- Verify your SPF record syntax is correct
- Avoid modifying forwarded messages
- Use forwarding providers supporting SRS and ARC
- Review DMARC reports regularly
- Test delivery across multiple providers
- Consider hosted email instead of forwarding-only setups
How to Fix Forwarding-Related DMARC Failures
Use Proper Hosted Email Instead of Simple Forwarding
The best long-term solution is usually:
- proper mailbox hosting
instead of
- forwarding-only setups
Hosted mailboxes maintain full authentication chains more reliably.
Ensure DKIM Is Enabled
DKIM gives forwarded mail a better chance of passing DMARC even if SPF fails.
Always verify:
- DKIM signing enabled
- public DNS keys published
- signatures validating properly
Use Forwarding Providers That Support SRS
If you must forward mail:
choose systems supporting:
- SRS
- ARC
- modern authentication preservation
Avoid Modifying Forwarded Messages
Do not:
- rewrite subjects
- append disclaimers
- inject tracking text
These changes often invalidate DKIM signatures.
Monitor DMARC Reports Regularly
DMARC reports help detect:
- forwarding failures
- spoofing
- unauthorized senders
- alignment problems
When This Goes Wrong
Forwarding-related DMARC issues often worsen because of:
Multiple Forwarding Layers
Each forwarding hop increases authentication complexity.
Old Registrar Forwarding Systems
Some older forwarding services were designed before modern DMARC enforcement existed.
Misconfigured SPF Records
Too many includes or invalid syntax can create failures.
Expired DKIM Keys
Rotated or outdated keys invalidate signatures.
Aggressive DMARC Policies
A reject policy without proper testing can unintentionally block legitimate forwarded mail.
Should You Stop Using Email Forwarding Entirely?
Not necessarily.
Forwarding still works in many situations.
However, businesses increasingly benefit from:
- hosted mailboxes
- proper outbound authentication
- provider-managed email infrastructure
Simple forwarding alone is becoming less reliable in modern email ecosystems.
Final Thoughts
Forwarded emails fail DMARC checks because forwarding changes how email authentication behaves behind the scenes. SPF commonly breaks during forwarding, and DKIM may fail if the message gets modified along the way. Once both fail, DMARC enforcement can reject the email entirely.
As providers continue strengthening anti-spoofing protections, businesses relying heavily on simple forwarding systems may encounter more delivery issues over time.
Understanding how SPF, DKIM, DMARC, SRS, and ARC interact is now essential for maintaining reliable email delivery.
NameSilo provides domain management tools, DNS management, and email configuration flexibility that help businesses maintain proper SPF, DKIM, and DMARC setups. Whether you are using email forwarding, Google Workspace, or hosted business email, NameSilo gives you the DNS control needed to improve authentication and deliverability.
NameSilo Staff
The NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.