What is an SPF Record SoftFail vs. HardFail (~all vs. -all)?
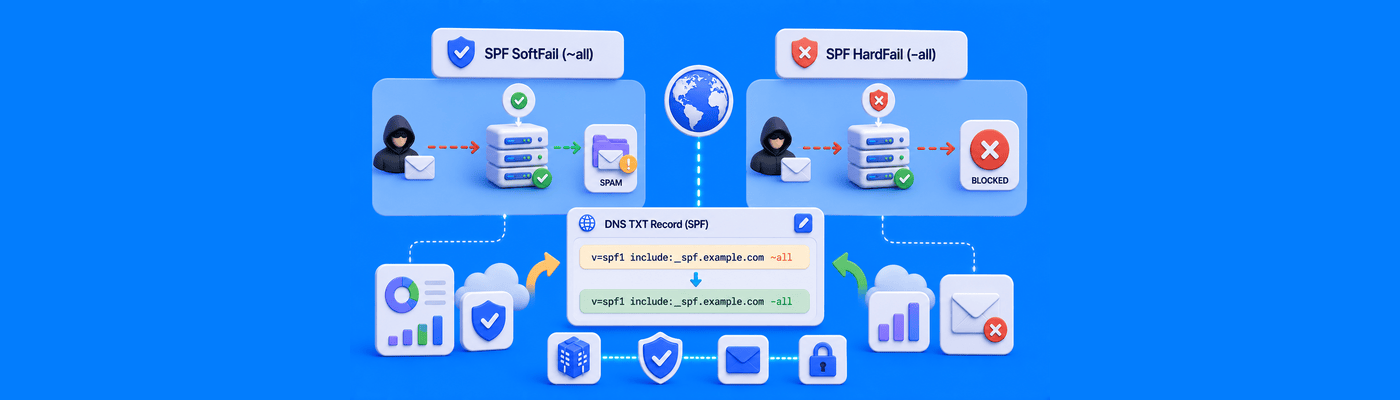
The difference between an SPF SoftFail (~all) and a HardFail (-all) lies in how strictly unauthorized emails are penalized. A SoftFail instructs receiving servers to accept unauthorized emails but flag them as suspicious, routing them to spam. A HardFail tells servers to completely reject and drop unauthorized emails immediately.
The Enforcement Mechanism Switch
Every SPF record ends with a qualifier that tells receiving servers what to do with mail from unlisted sources:
Qualifier | Symbol | Action | Enforcement Level |
Pass | (none) | Deliver normally | N/A |
Neutral | ?all | Treat as unverified | None |
SoftFail | ~all | Accept, mark suspicious | Moderate |
HardFail | -all | Reject outright | Strict |
The final character, tilde or hyphen, is the single switch that determines how aggressively your domain protects itself against spoofing.
Analyzing the SoftFail (~all)
Example record:
v=spf1 include:spf.titan.email ~all
SoftFail tells receiving mail servers: "If a message claims to be from this domain but doesn't match my authorized senders, deliver it anyway, but treat it with suspicion." Most receivers route SoftFail failures to the spam or junk folder rather than blocking them outright.
Why this matters during setup: SoftFail acts as a safety net. If you forgot to authorize a legitimate sending service, mail from that service still reaches the recipient's inbox, just filtered into spam, rather than disappearing entirely. This gives you time to notice and fix the gap.
SoftFail is the industry-standard starting point for any new SPF deployment.
Analyzing the HardFail (-all)
Example record:
v=spf1 include:spf.titan.email -all
HardFail is an absolute instruction: "If a message doesn't match my authorized senders, reject it. Do not deliver it under any circumstances." Compliant receiving servers drop the message before it reaches an inbox, sometimes returning a bounce notification to the sender.
This is the strongest anti-spoofing configuration SPF offers. Attackers attempting to forge your domain get blocked at the server level, not just filtered.
Decision Framework: When to Switch
Phase | Recommended Qualifier | Why |
Initial deployment | ~all | Catch missed senders without losing mail |
Testing period (2-4 weeks) | ~all | Monitor DMARC reports for unexpected failures |
Stable sender list confirmed | -all | Maximum protection once safe |
Before switching to -all, confirm:
- Every legitimate sending service is included in your SPF record
- DMARC reports show no unexpected authorized senders failing
- No forwarding services relay mail without proper authorization
Only move to HardFail once verified data confirms your sender list is complete.
The Risk of Over-Enforcement
Switching to -all before your sender inventory is complete is the most common SPF deployment mistake.
What happens: A marketing platform you forgot to authorize sends a campaign on your behalf. Under -all, every message gets rejected outright. Under ~all, those same messages would have landed in spam, still recoverable and visible in reports. Under -all, they simply vanish.
Before/after comparison:
Testing phase:
v=spf1 include:spf.titan.email ~all
Full enforcement (after 2-4 weeks of clean DMARC reports):
v=spf1 include:spf.titan.email -all
Notice only the final qualifier changes. Everything else in the record stays identical.
What This Means for You
When adding SPF records for NameSilo Email via Titan, start with ~all and monitor deliverability. NameSilo's DNS Manager automatically handles quoting for TXT record values, so you can paste your SPF string directly without manual formatting.
Frequently Asked Questions
What does tilde all mean in an SPF record?
SoftFail: unauthorized mail is accepted but marked suspicious.
What is the difference between softfail and hardfail?
SoftFail flags to spam; HardFail rejects the message outright.
Does SPF hardfail stop phishing?
It blocks domain spoofing via SPF but not all phishing vectors.
Can softfail cause emails to go to spam?
Yes. Many receivers route SoftFail failures directly to spam.
When should I change my SPF record to dash all?
After 2-4 weeks of clean DMARC reports confirming all senders.
What does a question mark all mean in an SPF record?
Neutral: no enforcement, treated as unverified with no penalty.
How do I format an SPF record string?
v=spf1 include:provider.com ~all as a single TXT record value.
How do I save security strings at NameSilo?
DNS Manager, add TXT record, host @, paste your SPF string.
NameSilo Staff
The NameSilo staff of writers worked together on this post. It was a combination of efforts from our passionate writers that produce content to educate and provide insights for all our readers.